SIEM · NetFlow · IDS · NIS2
Logs, Network Traffic and NIS2
on Your Own Server
FlowPro NG collects logs from your servers and network devices, analyses NetFlow and inspects traffic with the Suricata IDS. It alerts you to attacks and vulnerabilities and prepares the evidence for your NIS2 audit. Your data never leave your network.
100% on-premises. Free 14-day Enterprise trial, no credit card.
- 10:42:07critIDSFortiOS SSL-VPN exploit attempt (CVE-2024-21762) from 203.0.113.48
- 10:41:55highAUTHSSH brute force: 214 failed logins in 5 min from 198.51.100.23
- 10:41:31highFLOWHorizontal port scan 192.0.2.77 → 10.20.0.0/24
- 10:40:58medCVECISA KEV: Cisco ASA/FTD CVE-2025-20333 matches 3 assets
- 10:40:12medDNSPossible DNS tunnel from 10.20.4.15 (avg 412 B/query)
- 10:39:44lowFIM/etc/sudoers modified on web-02
Built on proven open-source foundations
ElasticsearchClickHouseKafkaSuricataT-Pot
- Tools & Modules
- 30+
- Tools & Modules
- Compliance Frameworks
- 6
- Compliance Frameworks
- Automated Controls
- 130+
- Automated Controls
- Languages
- 3
- Languages
Platform
What FlowPro NG Watches
Six areas covered by a single FlowPro NG server. Your license decides which modules are on; the data stay on your side.
All Features- 01
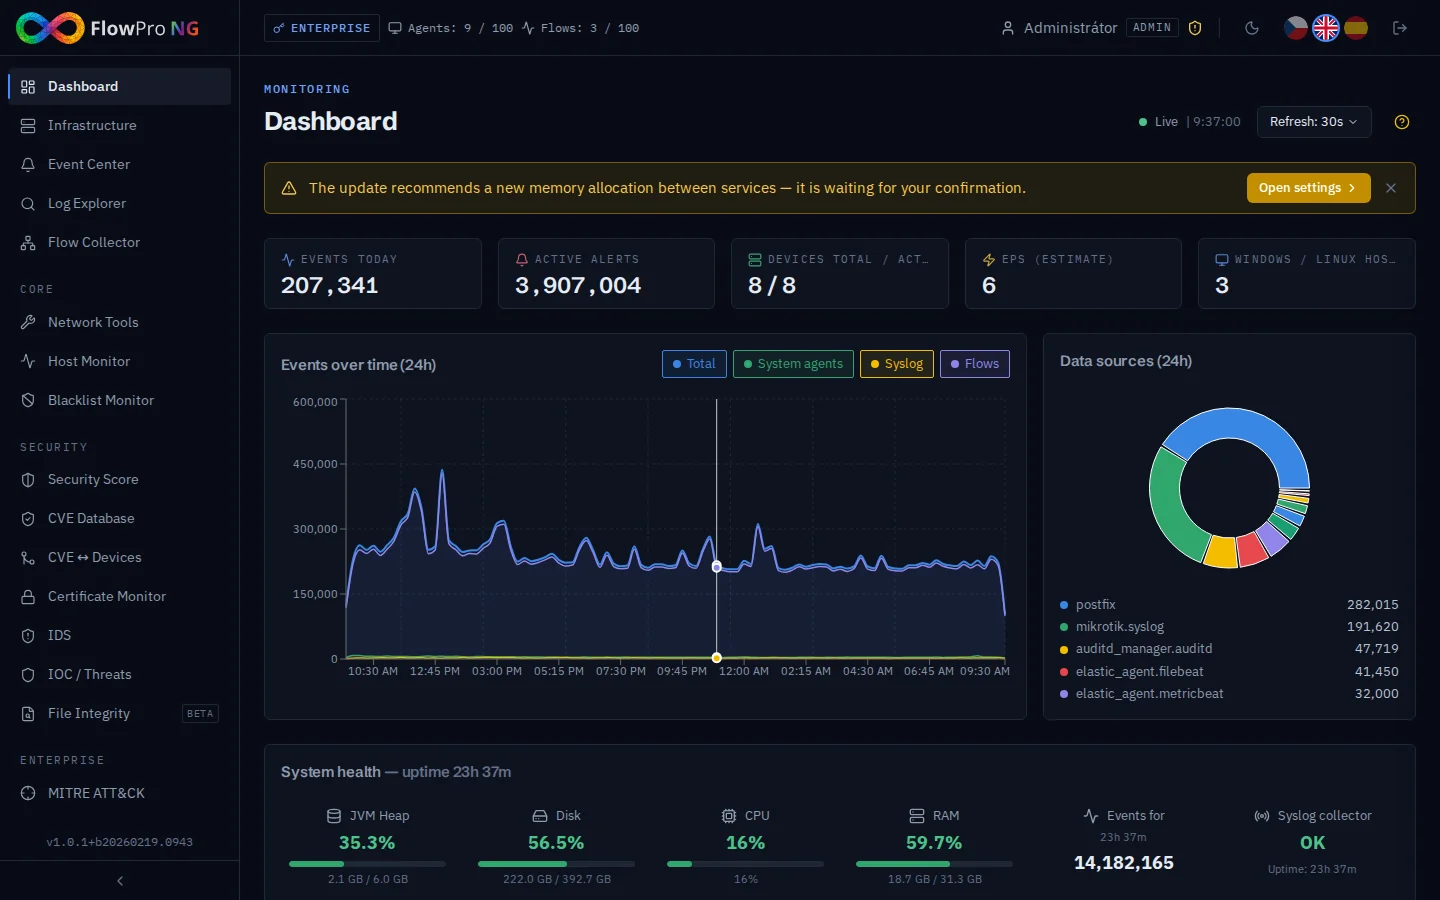
Real-Time Dashboard
Source health, alert trends and system metrics on one screen, updated live over WebSocket.
- 02
Intrusion Detection (IDS)
Suricata inspects your traffic including DNS, HTTP, TLS and FTP, and shows where each attack comes from.
- 03
Network Flow Analysis
NetFlow and sFlow are stored in ClickHouse via Kafka, so you can search billions of records. Anomaly detection flags port scans and data exfiltration.
- 04
AI-Powered Analysis
A local LLM (Ollama) or cloud AI sorts your logs by severity and suggests the next steps.
- 05
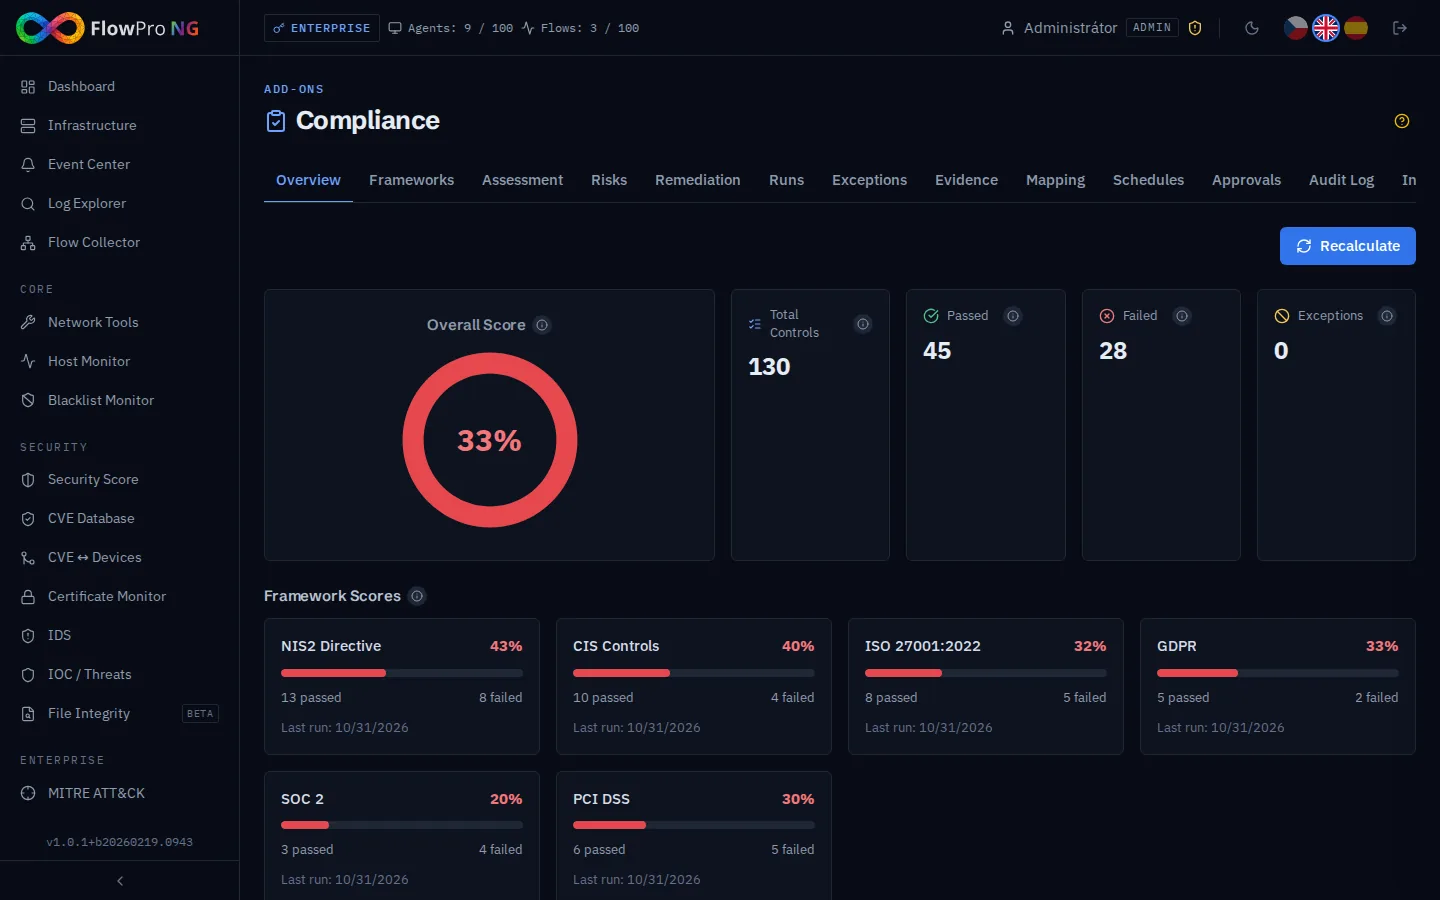
Compliance Automation
130+ automated controls for NIS2, CIS v8.1, ISO 27001, GDPR, SOC 2 and PCI DSS, with evidence and a PDF export for your auditor.
- 06
Honeypot Deception
T-Pot with 20+ honeypot types records SSH brute force, malware drops, credential harvesting and attacker behaviour.
How It Works
From Raw Events to a Decision
Everything runs on your own server. Logs, flows and alerts never leave your network.
- 1
Sources
Servers, workstations, firewalls and routers.
Elastic AgentSyslogNetFlow / sFlow - 2
Ingest
Parsing, normalisation and a queue that loses nothing.
LogstashKafkanfacctd - 3
Storage
Logs and metrics in Elasticsearch, flows in ClickHouse.
ElasticsearchClickHouse - 4
Detection
Rules, IDS signatures, flow anomalies and AI.
1,500+ rulesSuricataAI - 5
Response
Alerts, playbooks and evidence for NIS2.
E-mailSlackTelegramWebhook
NIS2 Compliance Pack
NIS2 Audit Without Spreadsheets
- 6 frameworks NIS2, CIS v8.1, ISO 27001, GDPR, SOC 2 and PCI DSS.
- 130+ automated controls evaluated continuously from the data FlowPro already collects.
- Evidence and PDF export ready for your auditor, in Czech, English or Spanish.
Free 14-Day Enterprise Trial
Install it on your own server with every module enabled and no credit card. After 14 days it switches to the free version.